Scenario Signal Ranking™ (SSR™)
Discover how PRIPEX's Scenario Signal Ranking™ (SSR™) framework evaluates multiple plausible institutional futures to improve strategic positioning under uncertainty.
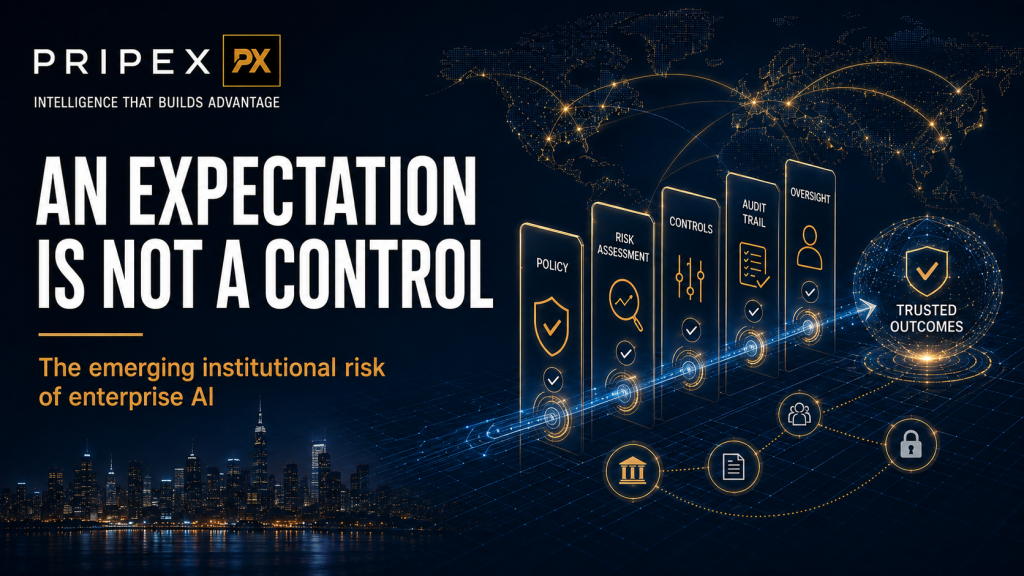
Why are responsible-AI policies and expectations not enough to control enterprise AI risk?
Responsible-AI principles, training and staff expectations establish intent, but they do not by themselves constitute an operating control system. As AI enters authoritative research, advice, knowledge and decision workflows, institutional reliability requires controls embedded into the workflow through ownership, inventory, provenance, validation, permissions, approval, monitoring, auditability, exception handling and release governance.
Table of contents [Show]
Organizations are writing responsible-AI principles, training staff and telling employees to verify AI-generated work. Those steps matter. But they do not, by themselves, constitute an operating control system.
The strategic risk appears when AI moves from experimentation into authoritative research, advice, knowledge and decisions. At that point, reliability cannot depend mainly on whether individual users remember to be careful. It must be designed into the workflow through ownership, inventory, provenance, validation, permissions, approval, monitoring, auditability, exception handling and release governance.
In July 2026, the Financial Times reported that several PwC Middle East thought-leadership reports contained fabricated or unreliable citations, misattributed claims and unverifiable sources in work that appeared heavily AI-assisted. PwC said it was correcting a limited number of supporting citations and that it expected staff to follow quality-control processes. The same reporting pointed to earlier retractions or corrections involving other major professional-services firms.
These cases should not be used to infer the precise internal control failure at any named firm. They do, however, expose a broader institutional tension: an organization can have quality expectations and responsible-AI policies while defective output still reaches publication.
A hallucinated citation is a model-output failure. Allowing that citation into a consequential report is an institutional-control failure. The distinction is crucial. Better models may reduce some errors, but they cannot decide who owns a workflow, which sources are authoritative, what evidence must be retained, who may approve release, what permissions an agent should have, or what happens when validation fails.
That is why enterprise AI governance is increasingly a management-system problem rather than simply a model-quality problem.
| Expectation | Embedded control |
|---|---|
| AI outputs must be accurate. | Material claims require source provenance and independent validation before release. |
| Humans remain accountable. | A named owner and approval authority are assigned to each material AI-enabled workflow. |
| Sensitive data must be protected. | Data classifications, permissions and approved-tool boundaries are enforced. |
| AI use must be transparent. | Defined provenance and disclosure fields are captured at required workflow stages. |
| High-risk outputs receive human review. | Review scope, evidence, reviewer competence and completion criteria are specified. |
| Problems must be corrected. | Incident and exception processes trigger containment, correction, notification and learning. |
PwC Canada's February 2026 Trust in AI research found that 72% of surveyed organizations described responsible AI as a top priority, while 36% had no dedicated governance function. Sixty-five percent cited issues such as unclear ownership, difficulty inventorying AI systems and concern that governance could slow innovation. The report itself called for clear accountability, lifecycle controls, consistent monitoring and independent testing.
This is the institutional gap PRIPEX is concerned with: the distance between saying AI must be responsible and possessing an operating system that makes responsible behavior repeatable.
A requirement for 'human review' can easily become ceremonial. Review is a real control only when the organization defines who reviews, what evidence they inspect, what competence they need, which materiality threshold applies, what independence is required and how completion is evidenced. As output volume rises, undefined review also becomes a throughput bottleneck.
The stronger design is layered assurance: provenance at generation, automated checks where reliable, targeted independent validation, explicit approval and retained evidence.
When AI systems gain access to institutional knowledge, software tools and execution pathways, the risk expands. An agent may retrieve stale or superseded information, act beyond its authority, propagate one bad assumption across several systems, or make reconstruction difficult after the event.
Technical capability must therefore be separated from institutional authority. A system that can publish, send, change or approve should not be presumed authorized to do so.
ISO/IEC 42001 treats AI governance as a management system that must be established, implemented, maintained and continually improved. NIST's AI Risk Management Framework and its Generative AI Profile likewise emphasize operational risk management, testing, evaluation, verification and validation. The direction is clear: responsible-AI language is becoming the starting point, not the finish line.
As access to powerful AI becomes more common, reliable institutional execution becomes a differentiator. The scarce asset is not merely intelligence generation. It is the ability to demonstrate that AI-enabled outputs and actions are trustworthy.
The PRIPEX Pro companion, From AI Policy to Embedded Control: Executive Assurance Brief, extends this analysis into an Expectation-to-Control Matrix, Executive Diagnostic, Control Maturity Ladder, Agentic-Enterprise Risk Map, 30/60/90-Day Action Plan and Board Evidence Pack.
This derivative was produced from the approved parent Strategic Intelligence Dossier and refreshed immediately before production. Primary institutional and standards sources are preferred; named-company incident reporting is used only where directly attributable.
Discover how PRIPEX's Scenario Signal Ranking™ (SSR™) framework evaluates multiple plausible institutional futures to improve strategic positioning under uncertainty.
Understand how the PRIPEX Signal Grid™ transforms complex global developments into structured institutional signals for stronger sovereign analysis and strategic positioning.